Skip to content
CareerBook ERP™Enterprise Education Operating System

Security & data protection

Your Data. Our Highest Priority.

CareerBook ERP™ is designed with layered security and resilient infrastructure to help protect institutional information and support reliable education operations — without claiming any system is risk-free.

CareerBook ERP™ · Enterprise Education Operating System (EEOS)

Whitepapers and audit packs are shared through an approved process — not as open public downloads.

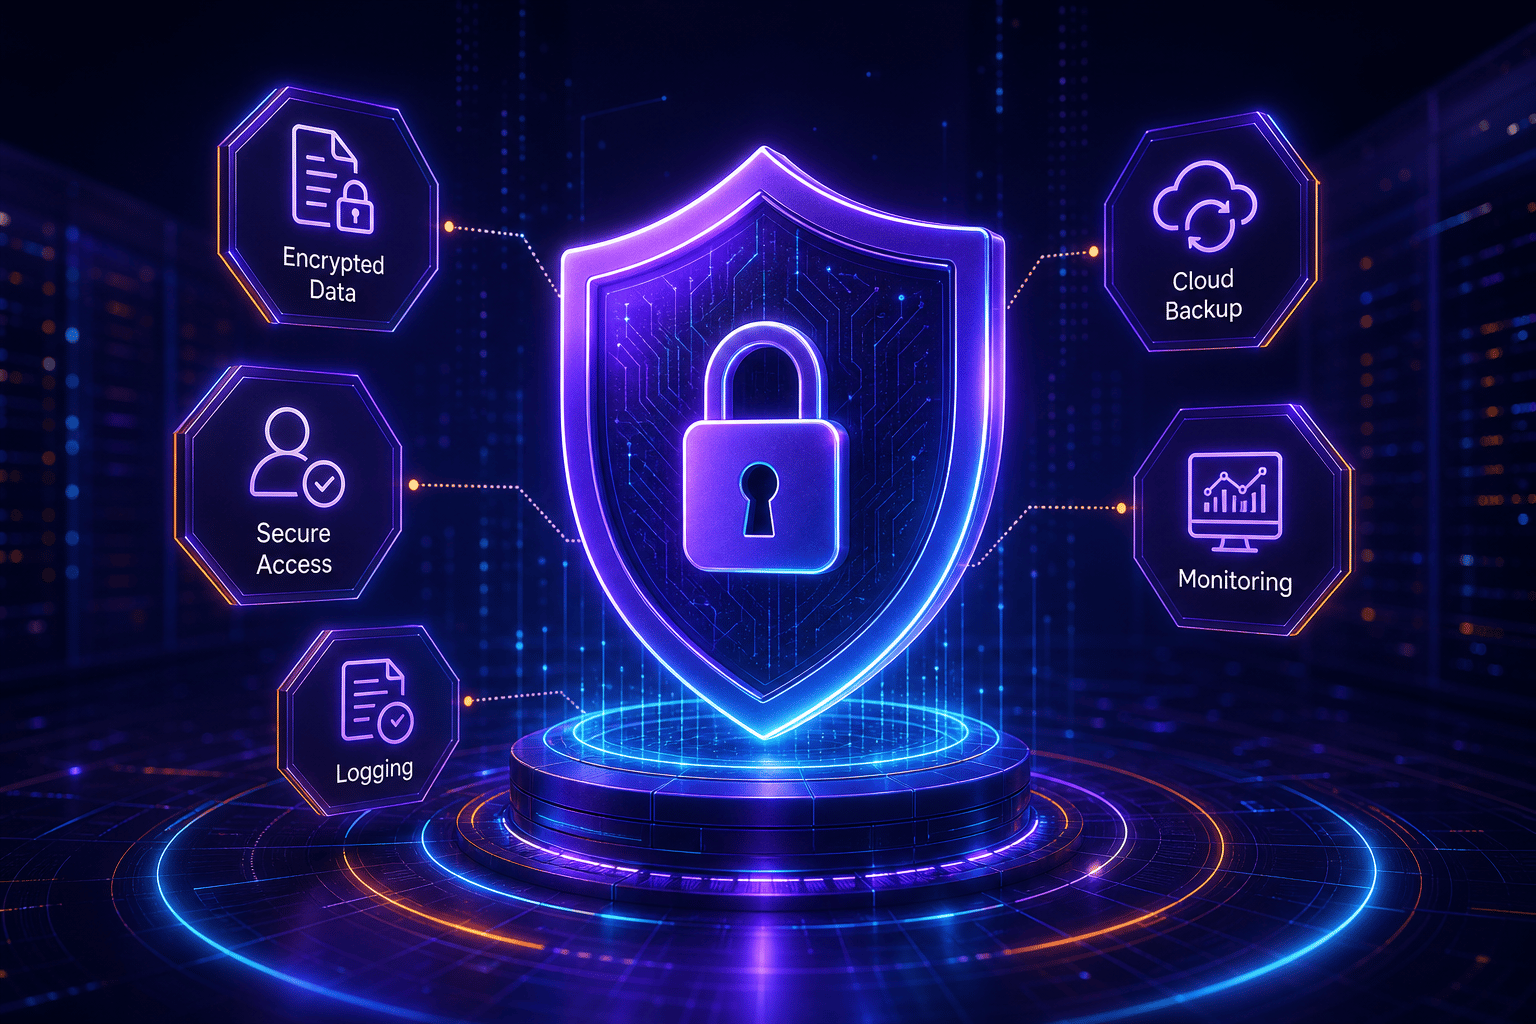
Illustrative CareerBook ERP™ security shield representing layered data protection
Illustrative security visual — not a live console or certification mark.

Institutions

Education groups — scale Confirm

Countries

Deployment footprint — Confirm

Stakeholders

Students & educators — Confirm

Bank Empanelments

Named banks — Confirm with team

Data Security Commitment

Layered controls — not a zero-risk claim

Scale, bank and absolute security claims publish only when marketing and compliance approve.

Enterprise-grade security

A Multi-Layered Security Approach

Practical controls across encryption, access, network and application security, privacy and monitoring. We describe measures — we do not claim immunity to all threats.

  • Data encryption

    CareerBook ERP™ is designed to protect data in transit and at rest. Exact algorithms, key management and coverage are confirmed for your deployment — not asserted as universal end-to-end for every path.

  • Identity & access control

    Role-based access and least-privilege patterns help ensure users see only what they are authorised to access. MFA, SSO and session controls are enabled where configured for the customer.

  • Network & application security

    Network controls, secure development practices and vulnerability management support the application layer. Specific WAF, DDoS or scanning schedules are shared through an approved security overview.

  • Activity logging & audit trails

    Selected user and administrative actions can be logged to support investigation and audit review. Exact event coverage, retention and tamper protections are confirmed per environment.

  • Data privacy & governance

    Customer data separation, access policies and privacy practices are designed around institutional ownership of data. Aligns with privacy principles discussed in our privacy and DPA materials.

  • Monitoring & incident response

    Operational monitoring and escalation paths help teams respond to issues. Hours of coverage, alert routing and response commitments are defined in your service arrangements — not assumed as 24/7 from this page alone.

Trust & compliance

Global Standards. Proven Compliance.

Registrations, audits, empanelments and certifications are different signals. Logos and absolute claims appear only when scope, validity and permission are confirmed.

  • CertificationSee certifications

    ISO Frameworks

    View details →
  • RegistrationSee certifications

    DPIIT / Startup Registrations

    View details →
  • RegistrationSee certifications

    GeM Registration

    View details →
  • RegistrationSee certifications

    Startup India / State Programmes

    View details →
  • AuditConfirm with team

    Independent / Big 4 Audit

  • EmpanelmentConfirm with team

    Bank Empanelments

  • PracticeDescribed

    Secure SDLC Practices

    View details →

“Security and data protection are central to how we evaluate education platforms — layered controls, clear accountability and honest status on certifications matter more than absolute promises.”

— Institutional IT leadership (Illustrative quote · Confirm)

Secure cloud infrastructure

High-Availability, Scalable and Secure

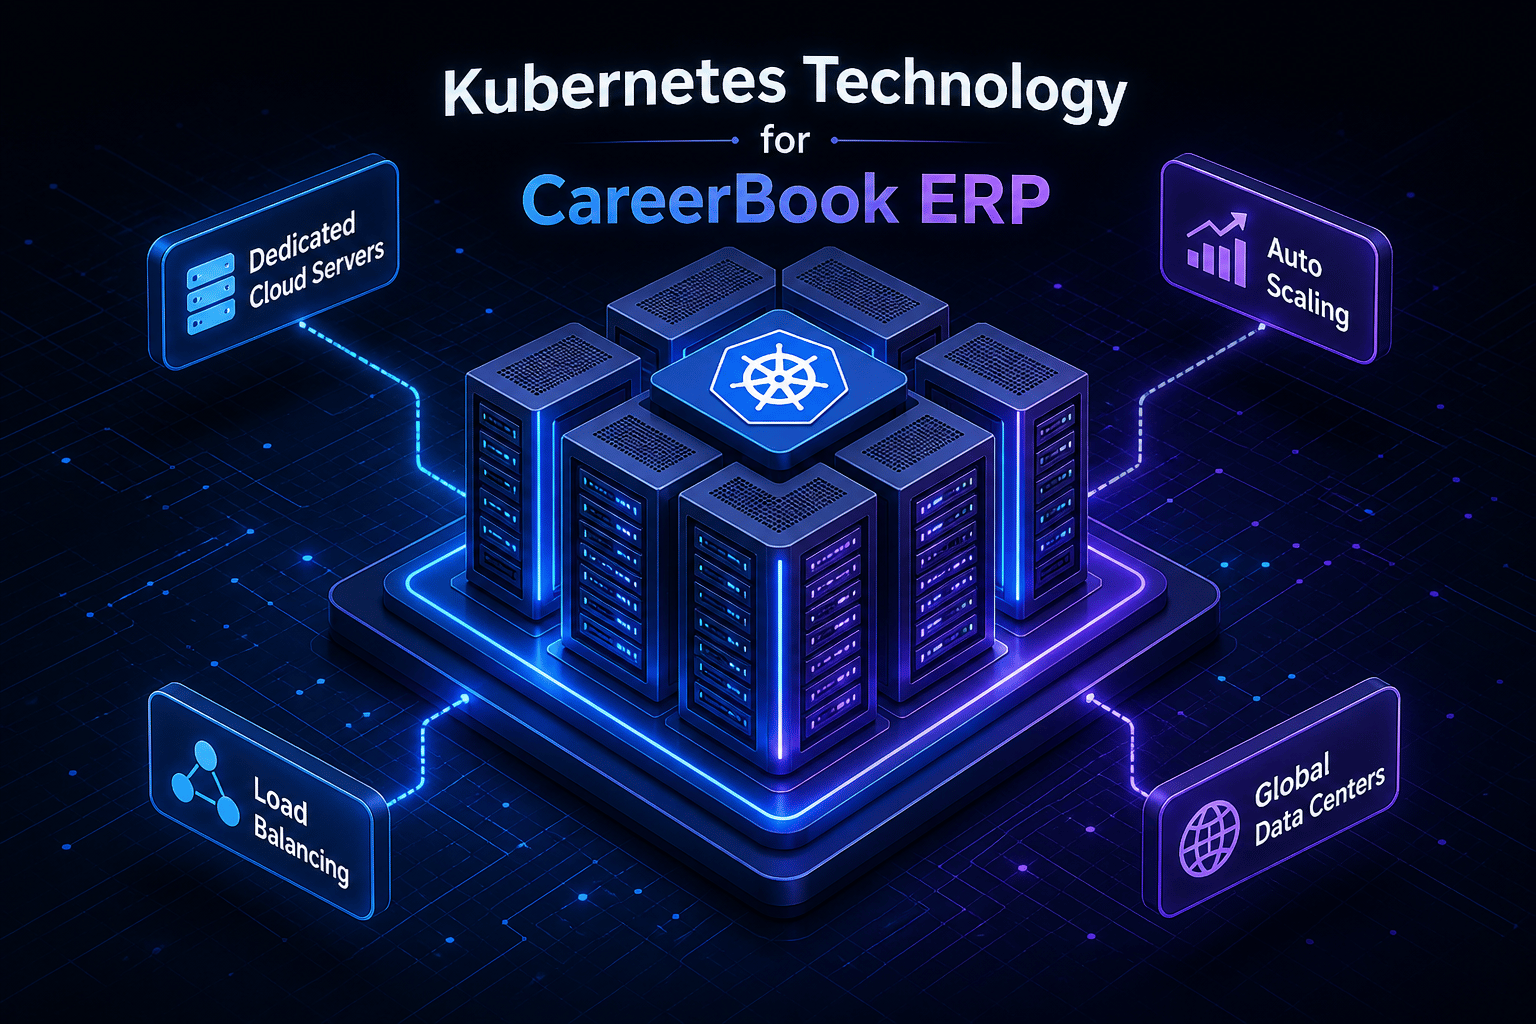
Dedicated cloud servers and Kubernetes-based technology where that model applies. The customer benefit is managed deployment and resilience — not a guarantee that Kubernetes alone equals security.

  • Dedicated cloud servers for managed CareerBook ERP™ deployments where that model applies
  • Kubernetes-based technology used to run and scale production workloads where confirmed
  • Controlled environments intended to support isolation boundaries appropriate to the tenancy model
  • Capacity and resilience planning discussed with customers during onboarding
  • Operational monitoring of platform health — ownership and hours confirmed per engagement
Product Architecture
Illustrative Kubernetes-based cloud infrastructure for CareerBook ERP™
Illustrative infrastructure graphic — provider logos and topology omitted pending Confirm.

Backup & disaster recovery

Your Data is Always Safeguarded

Backup frequency, retention, restoration testing, RTO and RPO are confirmed per engagement — not promised as zero-loss or uninterrupted availability from this page alone.

  • Automated backups

    Scheduled backup jobs form part of the operational design. Frequency and retention are confirmed for your environment.

  • Separated storage

    Backup copies are intended to be stored separately from primary workloads. Geographic separation is confirmed where applicable.

  • Disaster recovery plan

    DR planning covers how services are restored after a serious disruption. Scope and ownership are engagement-specific.

  • Restoration capability

    Restoration procedures exist so teams can recover data. We do not promise instant or zero-loss recovery without tested commitments.

  • Regular testing

    Restoration and DR exercises should be performed on an agreed cadence. Evidence can be shared through an approved overview process.

Accountability & operations

Transparency. People. Monitoring.

Complete Transparency

Logging supports investigation and audit review. Exact event coverage is confirmed per tenant.

  • Authentication events. Logins and access attempts where captured by the platform.
  • Record changes. Create, update and delete actions on selected business records.
  • Administrative actions. Configuration and privileged changes by authorised administrators.
  • Financial activity. Payment and fee-related events where finance modules are in use.
  • API activity. Selected API calls for integrations under customer configuration.
  • Session context. Device or IP context may be recorded where enabled for investigation support.
Trusted People. Strong Processes

Organisational safeguards complement technical controls. Screening scope confirmed before stronger public wording.

  • Relevant staff undergo background verification, including police clearance where applicable to role and location
  • Access to production systems follows need-to-know and joiner/mover/leaver controls where established
  • Confidentiality commitments form part of employment and contractor arrangements
  • Security awareness and secure-development practices are part of how teams work
  • Code review and change processes support safer releases — details available in a security overview

Real-Time Monitoring

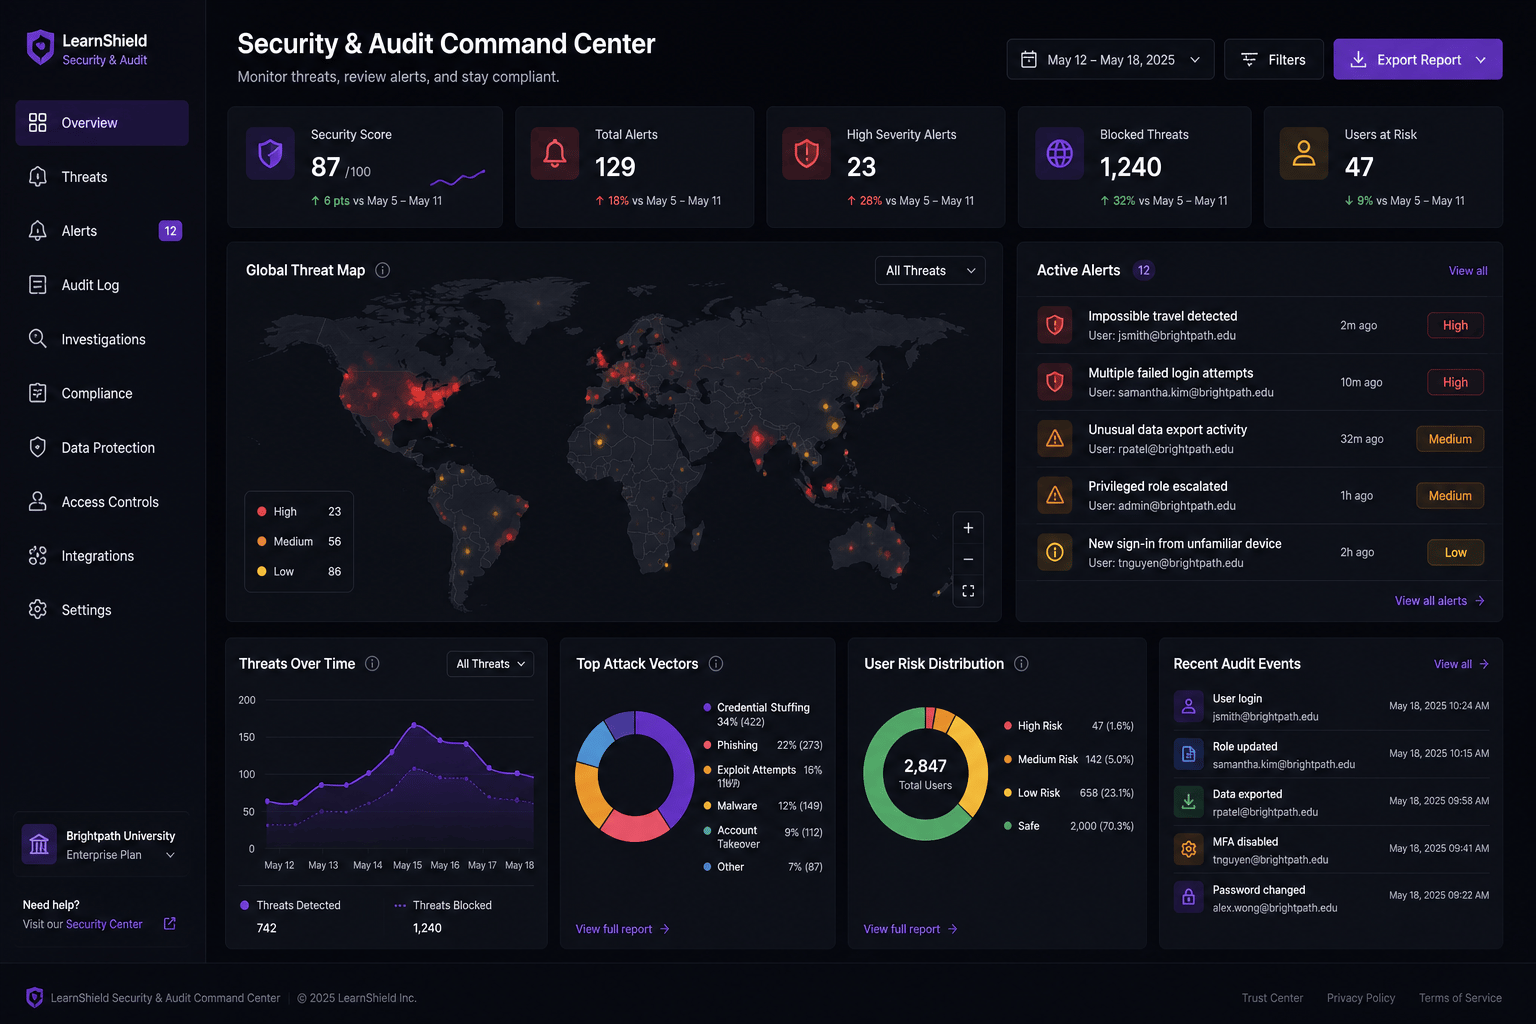
Operational awareness for managed services. The console below is illustrative — not a live Security Command Center.

Illustrative Security and Audit Command Center dashboard
Illustrative · synthetic data
  • Platform health and availability signals for managed services
  • Alerting routes for operational and security-relevant events where configured
  • Defined escalation to responsible teams — hours depend on your service package
  • Incident handling aligned to internal procedures; specifics shared under NDA when required

Security FAQs

Who owns institutional data in CareerBook ERP™?

Your institution owns its data. CareerBook ERP™ acts as a service provider / processor under applicable agreements. Data export and processing terms are covered in contracts and privacy materials.

Is CareerBook ERP™ 100% secure?

No system can honestly claim to be immune to all threats. We describe layered controls, operational practices and continuous improvement — not “unhackable” or “zero risk” guarantees.

Can we receive a detailed security overview?

Yes. Institutional buyers can request a security overview. Confidential architecture details, audit reports and penetration-test findings are shared through an approved process, often under NDA.

Do you support privacy frameworks such as DPDP or PDPL?

Controls are designed with privacy principles in mind (including India DPDP and regional PDPL/GDPR-oriented practices). Formal assessments and applicability to your jurisdiction are confirmed during contracting.

Where can I see certifications and registrations?

See the Certifications & Registrations page for frameworks and status notes. Only current, approved credentials should be treated as verified.

Built on Trust. Secured for the Future.

Talk with our team about CareerBook ERP™'s security controls, infrastructure, backup arrangements and audit information relevant to your institution.

  • Secure Institutions
  • Protected Students
  • Reliable Operations
  • A Brighter Future